

Authentication
API keys
Create, use, rotate and revoke HyperMemory API keys
An API key is a long-lived credential for servers, scripts, CI and agents that can’t run a browser sign-in. For interactive clients, prefer OAuth: there’s nothing to copy, store or rotate.
Key format
| Property | Value |
|---|---|
| Prefix | hm_ |
| Body | 64 lowercase hexadecimal characters |
| Shown | Once, when you create it |
| Stored | Only as a keyed hash (HMAC-SHA256). HyperMemory can’t show it again. |
In lists and logs a key appears by its prefix — the first 11 characters followed by ....
Create a key
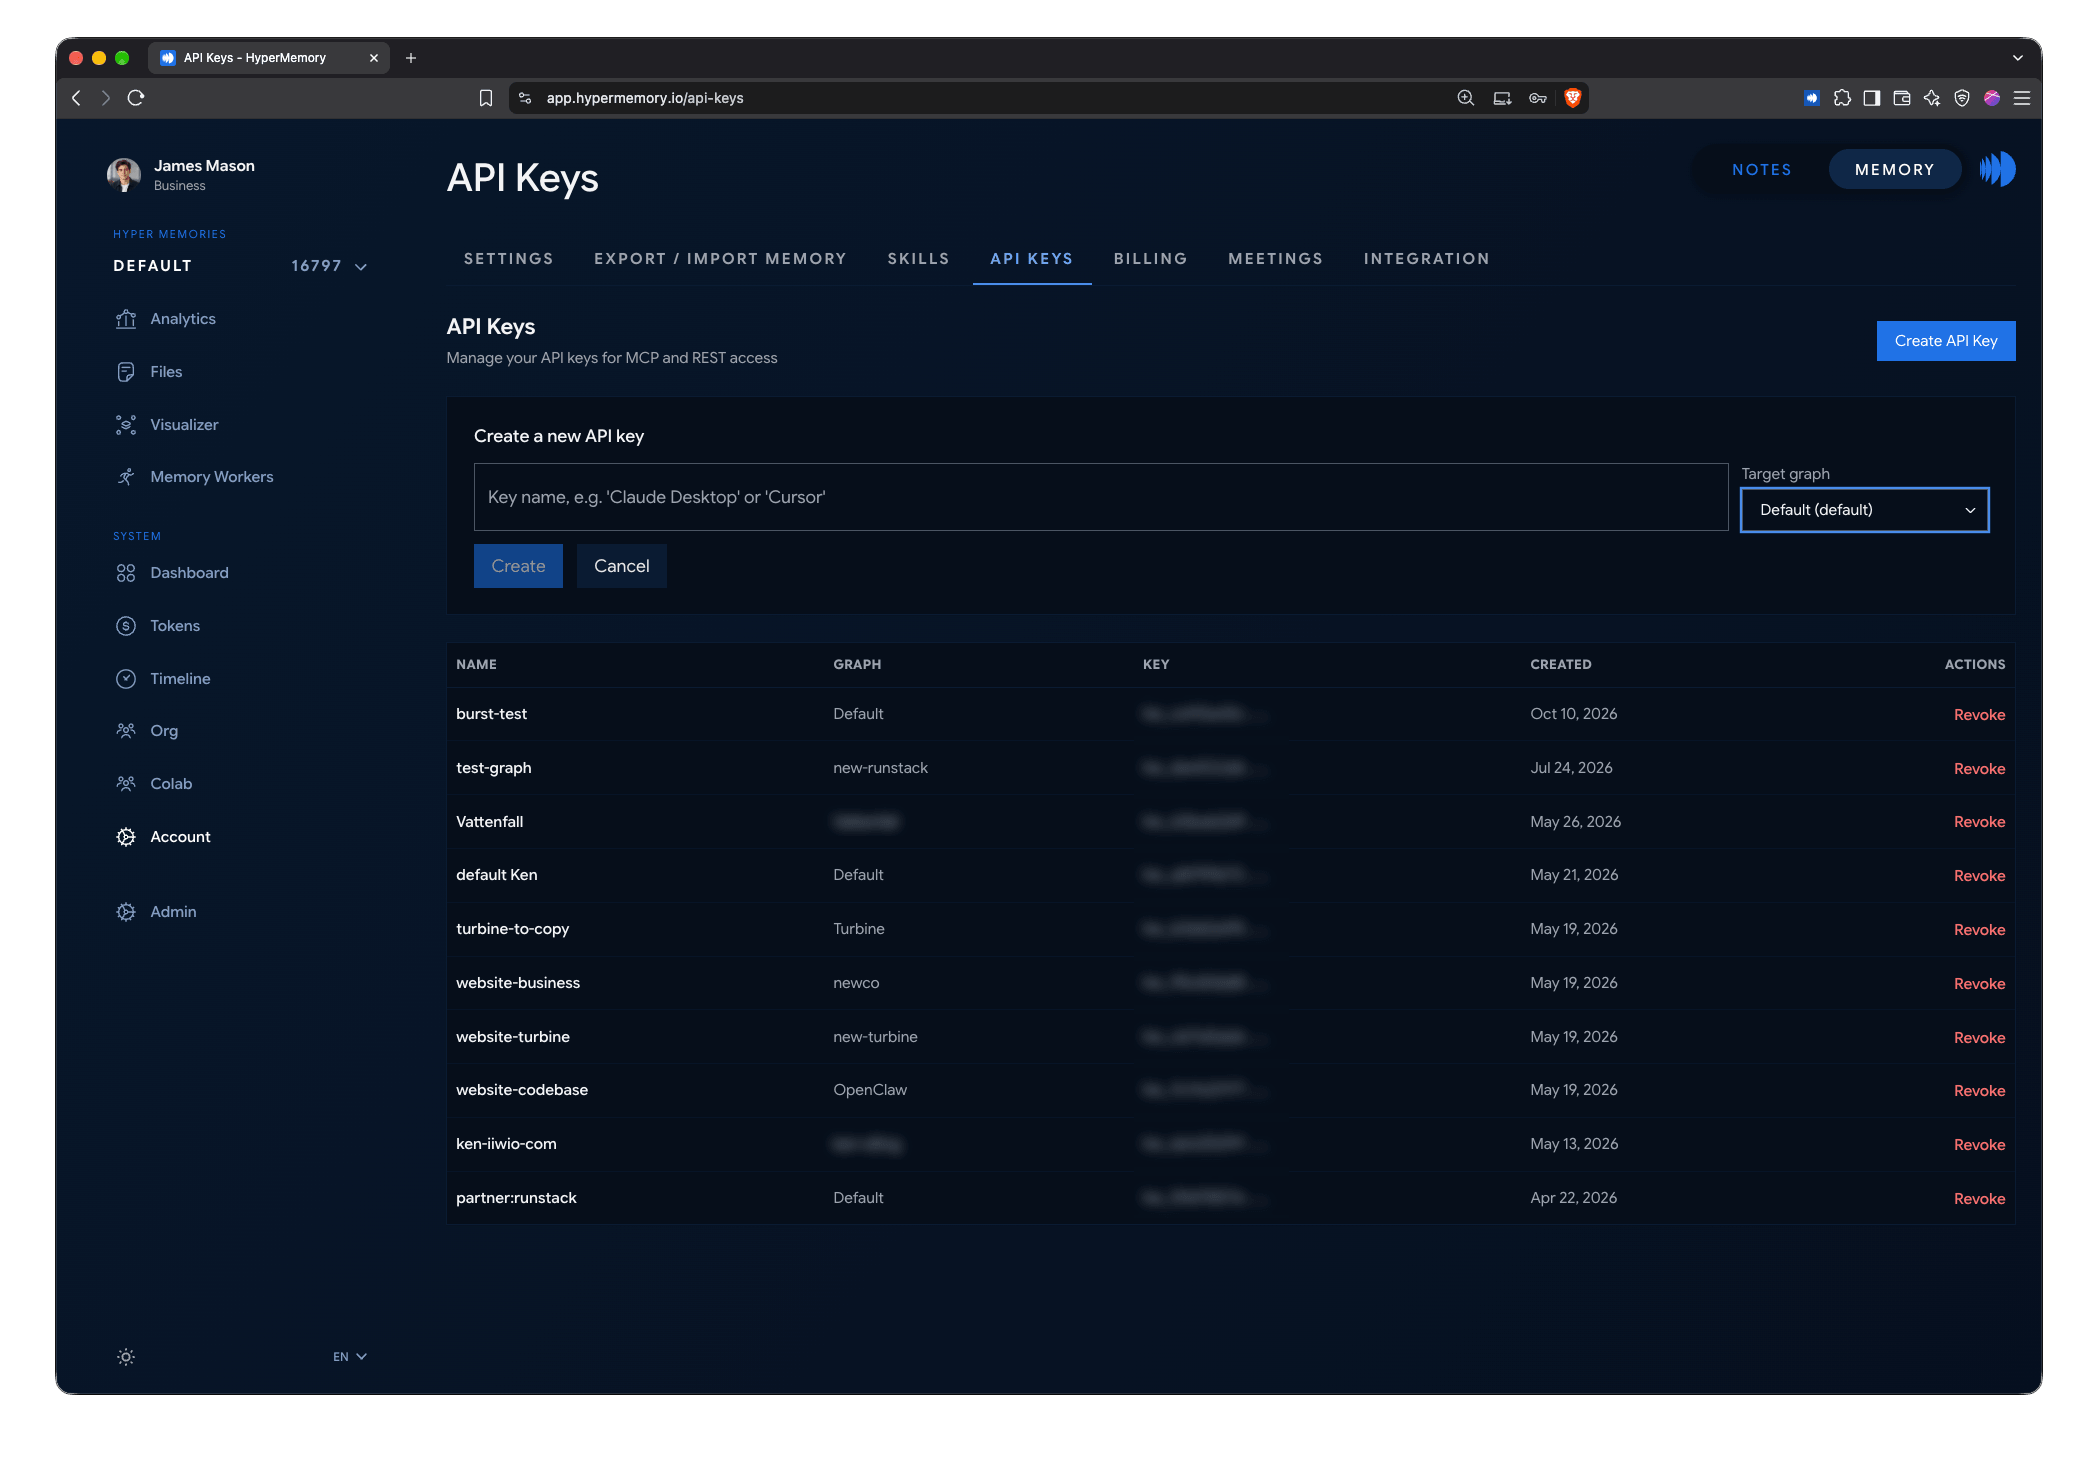
Create, copy and revoke keys on the API Keys page.
Open API Keys
In the dashboard, open Account → API Keys.
Name it and pick a graph
Give the key a name (up to 100 characters) that says where it's used, such as ci-nightly or support-bot. Choose the memory graph it can access; if you don't, it uses your default graph.
Copy it
Copy the key right away. The page also shows ready-to-paste MCP configuration with the key filled in.
Each key is bound to one graph. To give an agent access to two graphs, create two keys.
Use a key
Send it as a Bearer token on MCP and REST requests:
Authorization: Bearer hm_YOUR_KEYThe hm CLI and most integrations read it from the environment:
export HYPERMEMORY_API_KEY=hm_YOUR_KEYOr store it in the CLI’s keyring with hm login --api-key.
Rotate a key
- Create a new key bound to the same graph.
- Update every client to the new key.
- Revoke the old key.
Revoke a key
Open API Keys and choose Revoke next to the key. Revocation is immediate: the next request with that key gets 401.
What a key can do
A key acts as you, on the graph it’s bound to, with your plan’s limits. A key bound to a graph that has become read-only after a downgrade gets 401 graph_frozen until you upgrade.
Keys created in the dashboard can read and write. See Permissions for how organization roles and read-only access work.